What Is a Data Broker — and Why Is It Selling Information About You?
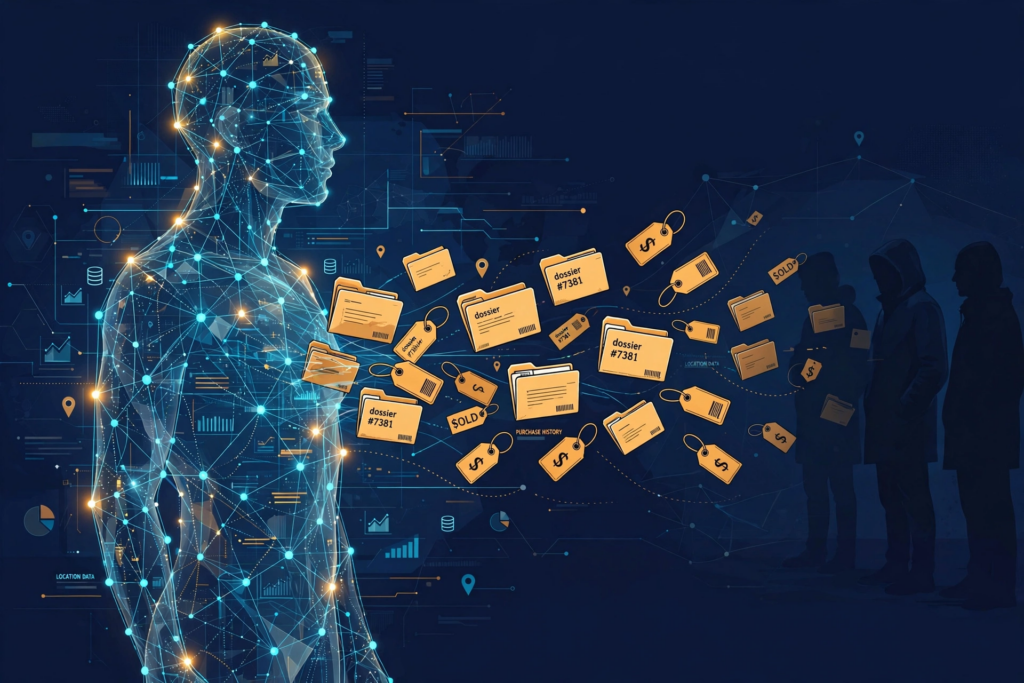
There’s a company that knows where you were last Tuesday, what you bought last month, and roughly how much money you make. You’ve never heard of it. You’ve never given it your information. You’ve never agreed to anything it does.
That company is a data broker. There are roughly 750 of them operating in the United States, according to the Privacy Rights Clearinghouse and the Electronic Frontier Foundation. Most of them have never sent you an email, shown you an ad, or appeared in your life in any way — except in the profile they’ve built of you, which they sell to anyone willing to pay.
This is how that industry works, who buys what it sells, what the law actually says about it, and what you can realistically do.
What a data broker is, in one paragraph
A data broker is a company whose product is information about you. It collects personal data from many sources, assembles it into detailed profiles of individuals and households, and sells those profiles — or slices of them — to other businesses. The defining feature: you are not the customer. You are the inventory. Most people have no direct relationship with any data broker, which is why the industry stayed invisible for so long. The Federal Trade Commission’s landmark 2014 report on the industry was literally titled “Data Brokers: A Call for Transparency and Accountability” — because at the time, almost nobody knew these companies existed.
Some names in the space: Acxiom (now part of the ad giant Interpublic), Epsilon, LiveRamp, LexisNexis. Oracle used to be one of the biggest players in advertising data — it shut that business down in 2024. Then there’s a long tail of smaller, specialized brokers you’ve truly never heard of, including location-data firms like Gravy Analytics, Venntel, Mobilewalla, X-Mode (now called Outlogic), InMarket, and Kochava. You’ll meet several of them again later in this article, because the FTC has spent the last two years taking them to court.
Where your data comes from
Brokers don’t hack you. They mostly buy, scrape, and infer. The raw material comes from five places:
1. Public records. Property deeds, voter registrations, marriage licenses, court records, professional licenses. This is the oldest feed in the business, and it’s perfectly legal to collect.
2. Your purchases. Loyalty cards, warranties you registered, magazine subscriptions, catalog orders. When a retailer sells its customer list — or a data broker buys a retailer — your shopping history becomes someone else’s product.
3. Your browsing and apps. Cookies, tracking pixels, and software kits (SDKs) embedded in ordinary mobile apps. An investigation standard finding, repeated across years of reporting: many free apps quietly send your location to third parties through advertising SDKs, often without making it clear. In 2026, the EFF found four advertising SDKs that share location by default whenever the app has permission.
4. Location data. Your phone’s GPS trail, bought in bulk. This is the most sensitive feed and the one regulators have finally started to bite on. More on that below.
5. Other brokers. Brokers buy from each other constantly, layering datasets together. Your voter file plus your purchase history plus your location trail becomes a single profile worth more than any piece alone.
The key move is inference: brokers don’t just collect facts, they manufacture new ones. From your location history they infer health conditions (regular visits to a cardiologist, a cancer center, a methadone clinic). From purchases they infer income, politics, religion, pregnancy. An October 2026 KFF Health News investigation found brokers inferring health conditions from phone location data and selling those inferences to advertisers — including marketers of unproven treatments.
Who buys it, and why
Advertisers and marketers are the biggest customers. They buy audience segments — “likely SUV buyers,” “new parents,” “people who visited a car dealership this week” — to target ads.
Insurers buy data to price risk. Employers and landlords buy background-check products built on broker data. Political campaigns buy voter enrichment. And government agencies buy it too: Venntel, a subsidiary of Gravy Analytics, sold location data access to government agencies — one of the facts that drew the FTC’s attention, since it meant location tracking without a warrant, laundered through a commercial sale.
None of this requires your permission in most of the United States. That’s the part people find hardest to believe, and it’s true: outside a handful of state laws, there is no general federal law that says a company needs your consent to collect and sell information about you.
When it goes wrong: the FTC’s enforcement record
For years the industry’s defense was that the data was “anonymized.” Regulators have stopped accepting that, because location trails are trivially re-identifiable — a handful of location points (home, work, gym) uniquely identifies almost anyone.
Since January 2024, the FTC has announced orders or settlements with five location-data companies:
- X-Mode Social (now Outlogic), January 2024 — sold location data that could reveal visits to clinics, places of worship, and shelters without informed consent. Banned from selling sensitive location data.
- InMarket, January 2024 — sorted people into ad audiences using location from its own apps. Banned from selling or licensing precise location data — the FTC called it a first.
- Gravy Analytics and Venntel, finalized January 2025 — bought location data from other suppliers and sold sensitive profiles, including geofenced lists of people who visited health care facilities. Barred from selling sensitive location data; ordered to delete historic location data.
- Mobilewalla, finalized January 2025 — collected location from real-time ad-bidding exchanges (even when it lost the auction) and built audience segments around visits to health clinics and places of worship. Barred from selling sensitive location data and from using auction data for anything but the auction — the first time the FTC alleged that collection itself was an unfair practice.
- Kochava, settled May 2026 — the FTC had alleged it sold location data from hundreds of millions of devices that could trace visits to health facilities and places of worship. The settlement bars selling sensitive location data without your affirmative, express consent. Notably: no fine.
The honest caveat, which privacy advocates keep repeating: each order binds only the company named. Settlements are not laws. Nothing stops the other ~745 brokers from doing the same thing tomorrow.
What the law says (as of late 2026)
There is no comprehensive federal privacy law in the United States. What exists is a patchwork — and it’s shifting fast:
The states moved first. Vermont created the first data broker registry back in 2018. As of mid-2026, seven states have data broker-specific laws: California, Oregon, Texas, Vermont, Montana, Connecticut, and New Jersey (whose registration rules take effect in 2027). The definitions don’t match from state to state, which is its own mess.
California’s Delete Act is the biggest deal. It created a public registry of data brokers (around 500 registered) and, starting January 1, 2026, a one-stop deletion platform called DROP — the Delete Request and Opt-out Platform. California residents can submit a single request that goes to every registered broker. Brokers have had to process those requests every 45 days since August 1, 2026, with penalties of $200 per request per day for non-compliance. In its first eight weeks, DROP drew 242,000 sign-ups. California has already issued its first Delete Act enforcement action: a $45,000 fine against a broker selling health-condition lists.
The federal efforts mostly stalled. In December 2024, the Consumer Financial Protection Bureau proposed treating data brokers like credit bureaus under the Fair Credit Reporting Act. In May 2025, it withdrew the proposal entirely. One federal law did land: the Protecting Americans’ Data from Foreign Adversaries Act (2024) bars brokers from selling Americans’ sensitive data to foreign adversaries, and in February 2026 the FTC sent warning letters to 13 data brokers reminding them that violations can carry penalties over $53,000 each. Separately, a Justice Department rule restricting bulk transfers of sensitive data to certain countries took effect in 2025.
Only six states ban the sale of precise geolocation data outright (Connecticut, Delaware, Maryland, New Jersey, Oregon, Virginia, per KFF Health News). In California, the governor vetoed such a bill in September 2026.
Bottom line on the law: if you live in California, you have a genuinely useful new tool. If you live anywhere else, your protections are thin — and most of what brokers do remains legal.
What you can actually do about it
Honest framing first: you cannot fully opt out of the data broker economy. Your public records exist. But you can shrink your footprint substantially. In order of effort:
Five minutes: Turn off precise location for apps that don’t need it (phone settings → privacy → location services). Turn off ad personalization on your phone (iOS: Settings → Privacy → Apple Advertising; Android: Settings → Privacy → Ads). These cut off the two richest feeds.
Thirty minutes: If you’re a California resident, submit a deletion request through the state’s DROP platform — one request hits every registered broker. Everyone else: visit the opt-out pages of the biggest brokers directly (Acxiom, Epsilon, and LexisNexis all have them; they’re deliberately hard to find, which tells you something). Also opt out of people-search sites — they’re the consumer-facing end of the same industry.
Ongoing: Consider a deletion service (DeleteMe, Kanary, Optery, Mozilla Monitor are the established names — this is a category description, not an endorsement; they charge a subscription to file opt-outs on your behalf, repeatedly, because brokers re-collect). Freeze your credit reports — it doesn’t stop data brokers, but it limits what identity thieves can do with the profiles that leak. And treat every “free” app’s location permission as a business transaction: you’re paying with your movements.
What doesn’t work: deleting your Facebook account, using incognito mode, or assuming a VPN hides you from brokers. Brokers don’t need your browsing — they have your purchases, your public records, and your phone’s GPS.
The bottom line
Data brokers exist because personal information is valuable and, in most of America, freely tradable. The industry ran for decades in the dark; it’s only in the last few years — through FTC enforcement, state registries, and California’s deletion platform — that daylight has started getting in. The profile of you is out there. You can’t delete it entirely. But you can now, for the first time, see the shape of the machine — and in California, push a button that makes a few hundred companies forget you at once. That’s not victory. It’s a start.
Sources: FTC, “Data Brokers: A Call for Transparency and Accountability” (2014); FTC enforcement announcements: X-Mode/Outlogic (Jan 2024), InMarket (Jan 2024), Gravy Analytics/Venntel (Dec 2024, finalized Jan 2025), Mobilewalla (Dec 2024, finalized Jan 2025), Kochava settlement (May 2026); KFF Health News investigation (Oct 30, 2026); California Privacy Protection Agency — Delete Act / DROP; Future of Privacy Forum / fintechlaw.ai regulatory landscape brief (Aug 2026); California Lawyers Association privacy-law update (2026); Protecting Americans’ Data from Foreign Adversaries Act (2024); CFPB Regulation V NPRM (Dec 2024, withdrawn May 2025).
Share on Facebook ↗ · Share on X ↗
Related reading
$6.3 Billion in 20 Minutes: The Numbers Behind the Biggest Hack in Crypto History, Visualized
Your Dashboard Is Green. Your Business Is Losing Money. What Are You Measuring?
Stop Copying and Pasting Your Business Data: A Practical Guide to Coupler.io